
EU Supervisors Rate Quantum Risk as High: What to Check on Crypto Custody and Exchange Choice
EBA, EIOPA and ESMA name quantum computers explicitly as a threat to blockchain cryptography in their autumn risk picture of September 23. What the paper says, which migration deadlines run to 2030, and three things you can check about your custody.




Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.
The three European financial supervisory authorities added quantum risk to their official autumn risk picture on September 23, 2026. Nothing about your holdings changes today, and the paper is not a warning about an imminent attack. What changes is the expectation placed on your provider: exchanges, custodians and banks in the EU now have to plan the migration of their encryption, and you can measure them against that.
This article sets out what the document actually says, which deadlines sit behind it, where the real attack surface lies for Bitcoin and Ether, and which three things you can check about your own custody without waiting for technology that does not yet exist.
What the EU supervisors wrote about quantum risk on September 23
Behind the paper stand the three European Supervisory Authorities, the ESAs: the banking authority EBA, the insurance authority EIOPA and the markets authority ESMA. Twice a year they publish a joint risk update in which the Joint Committee names the weak points of the EU financial system. The autumn 2026 edition appeared on September 23, and its core findings had been presented on September 10 at the Financial Stability Table of the EU Economic and Financial Committee. The statement is available in full at ESMA and at the EBA.
On quantum computing the text says the technology could transform the financial sector in central areas, from process optimisation through fraud and compliance monitoring to pricing. The same paragraph carries the flip side: the technology could equally create significant risks by undermining cryptographic systems that are used at scale to secure communications, transactions, databases and blockchains. Blockchains are named explicitly there, and not as a footnote to a banking topic.
The sentence that carries the urgency is a different one: the risks could materialise faster than any commercially viable application. In other words, the supervisors expect the ability to break old encryption to arrive before the economic benefit with which quantum computers are otherwise advertised.
Three weak points in one paper
The quantum topic does not stand alone. The ESAs name three fields: dependence on providers and infrastructure outside the EU, new technologies involving artificial intelligence and quantum computing, and the rapidly grown market for private credit. For crypto investors the first two fields are relevant, and they interlock. On the same September 23 ESMA additionally declared digital innovation a new supervisory priority from 2027, which shows that this is more than a one-off remark.
“Harvest now, decrypt later”: why intercepted data becomes a problem later
Harvest now, decrypt later describes an approach in which an attacker records encrypted data today and stores it, in order to decrypt it only once the necessary computing power exists. The attack therefore happens in two steps that can lie years apart.
For banking data, health records or contract documents that is the core of the problem, because their value does not expire. With a public blockchain the case is different and in one respect more uncomfortable: there, nobody has to intercept anything. The data lies open, permanently and retrievable by anyone. Whoever stores a copy of the chain today has everything they would need in ten years.
That is precisely why the distinction in the next section matters. The transaction history is always open. What decides the question is whether the public key belonging to a particular address is open as well.
Post-quantum cryptography: the migration deadline of end-2026 and who it binds
Post-quantum cryptography, abbreviated PQC, covers encryption and signature schemes that cannot be broken even by a powerful quantum computer. It rests on different mathematical foundations, and it is not about longer passwords.
The European timetable for this was not set by the Joint Committee. It comes from the NIS Cooperation Group, in which the member states work together. In June 2025 the group adopted a roadmap that the states endorsed. It provides for three stages: by the end of 2026 all member states should have begun the migration, meaning national strategies, inventories of the schemes in use and first migration steps. High-risk applications, which expressly include the financial sector, should be protected as early as possible and by 2030 at the latest. By 2035 the migration should reach as far as is practically feasible.
One point matters for placing this correctly: these deadlines bind member states, operators of critical infrastructure and supervised financial firms. As a private individual you are bound by no deadline. That is a relief, and at the same time it is the reason you have to look for yourself, because nobody migrates your self-custody on your behalf.
Elliptic curves, public keys and Bitcoin addresses: where the attack surface sits
Bitcoin and Ethereum sign transactions with schemes based on elliptic curves. A public key is computed from a private key, and that computation is easy in one direction and practically impossible in reverse. A sufficiently large quantum computer would make the reverse direction attackable, because a known method from quantum computing solves exactly this problem.
Here is the message for holders. With the address formats common today, the chain does not hold the public key itself, only its hash. The key becomes visible only when you spend from that address for the first time. As long as an address has only received, the information needed for this attack is not public.
That leaves two groups with a clearly raised attack surface. First, very old holdings from the early days, where the public key sits directly in the chain. Second, addresses that were used again and refilled after a spend, because from the first spend onwards the key stays permanently visible.
On the question of how far the hardware is from that point there is no reliable year, and this article deliberately names none. What is documented is that the estimates are moving towards lower effort: work published by Google Quantum AI in March 2026 concluded that breaking the 256-bit curves in use should require considerably fewer physical qubits than older models had assumed, by roughly a factor of twenty according to the reporting on that work. That is a correction to an estimate, not a date.
 Regulated crypto exchanges compared
Dependence on non-EU service providers: the second finding that hits your exchange
The finding that takes up more room in the paper than the quantum topic is dependence on providers outside Europe. The ESAs identify a persistently strong dependence on IT service providers and payment systems outside the EU, and point out that it remains visible in the financial infrastructures as well, where clearing, repo business and ratings are predominantly handled by entities outside the EU.
For you this is not an abstract subject, because a trading platform is first and foremost software. The servers, the custody system, the identity checks and often the settlement sit with service providers whose names appear in the terms and conditions rather than on the front page. When supervisors expect cryptographic migration, that whole stack has to move with it, and the migration is only as fast as the slowest supplier.
In practical terms: a platform licensed in the EU gives you a counterparty bound by European rules, and a supervisor able to ask questions. If the choice is still ahead of you, the comparison of regulated crypto exchanges breaks down the licences, the registered seat and the custody model for each provider. That does not replace reading the terms yourself, but it shortens the job considerably.
AI-assisted attacks: why phishing is the nearer risk than the quantum computer
In the same chapter the ESAs write that the rapid development of advanced AI systems could make cyberattacks more effective and harder to control, because attackers could find and exploit weaknesses at unprecedented speed. For insurers they expect more frequent and more severe claims as a result.
That ordering is worth holding on to, because public debate often runs it the other way round. Quantum risk is significant, and it has no date. Automatically generated phishing pages, convincingly written support messages and cloned voices on the phone are circulating today and cost holdings today. The same precaution works against both, and it is unspectacular: the private key never leaves the device on which it was created, and an approval is confirmed on a screen that does not belong to the sender of the message.
That is exactly the purpose of a hardware wallet: the signature is created inside the device, and the content of the transaction is displayed there. A compromised computer can then propose a false payment, but it cannot approve one unnoticed.
Exchange balance, hardware wallet or self-custody: what supervisors do not settle for you
The obligations arising from the risk picture are addressed to supervised firms. Where your coins sit therefore decides who carries the migration burden.
If the balance sits with a regulated exchange or a custodian, that provider carries the migration of its systems, and the supervisor can question it about them. In return you depend on its diligence and on its insolvency risk. If you hold the keys yourself, you carry the migration yourself, and in return nobody stands between you and your coins. A third variant is the split, in which an actively traded portion stays on the exchange while the long-term holding sits in self-custody.
What you can ask your provider
- Is there a published roadmap for post-quantum migration, and does it name years?
- Which parts of custody sit with service providers outside the EU, and who is your contact if something fails?
- Are deposit addresses generated fresh for each transaction or permanently reused?
- Can withdrawal addresses be locked and approvals tied to a second device?
- When was custody last audited, and is the result available to read?
The last three points take effect immediately, independently of any quantum debate. If the first question goes unanswered, that is no proof of negligence, but it does indicate how far the planning has got.
MiCA licence and custody duties: what you find in your provider's terms and conditions
Since the European regulation on markets in crypto-assets applies in full, service providers need an authorisation as a crypto-asset service provider, CASP in the wording of the regulation, in order to offer trading and custody. The authorisation brings duties that bite at exactly the point at issue here: client holdings have to be segregated from the firm's own funds, custody has to be documented, and there are reporting and contingency duties for outages and attacks.
These duties are the lever through which a supervisory finding reaches the provider. An ESA risk picture is not a law and sets no deadline for an individual firm. It does feed into supervisory practice, and that is where an observation turns into a question in an examination report. Which duties apply in detail and when the transitional rules run out is set out in our overview of the MiCA obligations for crypto firms.
For your own records one point matters more in practice than any debate about the regulation: write down which provider holds which assets and under which authorisation. If a provider changes its offering or leaves the market, you need that overview immediately.
 Hardware wallets compared
Moving wallets and the holding period: why a transfer between your own wallets is not a sale
Anyone who takes this as the occasion to move holdings from an old address to a new one, or from the exchange into self-custody, rightly asks the tax question. The basic rule in Germany is clear: a transfer between two wallets that both belong to you is not a disposal. There is no sale, so no gain arises, and the one-year holding period keeps running. Only a sale, a swap into another coin or a payment made with it is a taxable event.
In practice this rarely fails on the law and often on the documentation. A portfolio tracker that does not recognise a self-transfer as such books the outgoing leg as a sale and the incoming leg as a purchase. A gain that never existed then shows up in the report, and the holding period starts again inside the software. So anyone moving holdings marks the event in their tool as an internal transfer and keeps the transaction IDs. Which programs merge self-transfers reliably is shown by the comparison of crypto tax tools.
A second point concerns the sequence. If you are consolidating several addresses anyway, it is better done calmly than under time pressure, because every move is an operation in which an address can be copied down wrongly. The most common loss in this area has nothing to do with cryptography.
“Quantum-safe” coins and wallets: how to spot dubious offers
Every supervisory announcement carrying a technical buzzword produces offers that lean on it. The pattern is predictable, and so are the markers.
- An offer promises protection and asks you to enter your existing recovery words for it, for a migration or a check, say. That is a theft attempt in every case, without exception.
- A new token is advertised as quantum-safe and is therefore supposed to rise in value. The security properties of a protocol say nothing about the price of a token.
- A year is named from which existing schemes are said to be broken. No such figure is reliable at present, including in the supervisors' papers.
- There is time pressure, a countdown or an offer valid only today. A genuine protocol migration is announced and debated over months.
The protocols themselves work on this seriously, and visibly so. Proposals for quantum-resistant signature schemes are debated in open development processes, with specifications, testnets and objections. A migration of that size will surprise nobody who follows the developer channels of their own coin.
Quantum risk and custody: what to take away
The EU supervisors have moved a long-term risk into an ongoing supervisory process. That is good news, because it creates accountability where there was only debate before. Three steps follow for you, and none of them is urgent.
- Sort your addresses. Check whether you hold balances on addresses that have already been spent from, and whether you manage very old holdings from the early days. Those are the parts that are affected at all. If everything sits with a provider, first check who holds the keys there, and compare the custody model in the overview of regulated crypto exchanges.
- Harden your approvals. The nearer risk is the attack on you rather than on the mathematics. Tie withdrawals to a second device, fix address book entries and sign larger amounts on a device kept for that purpose alone. The differences between the devices are set out in the comparison of hardware wallets.
- Book your moves cleanly. When you reorder addresses, mark every self-transfer as such and keep the transaction IDs, so that the holding period does not restart in the report. Which programs handle that reliably is shown by the comparison of crypto tax tools.
And the sentence for calm: if the ability to break elliptic curves ever exists, your wallet will not be the first target. Ahead of it stand bank connections, government communications and the signatures that hold the internet together. That is why the topic appears in the risk picture of a financial supervisor and not in a warning notice to retail investors.
(As of September 25, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Transparency note: This article was produced with the assistance of artificial intelligence and reviewed by our editorial team before publication. All figures and claims were checked against the primary sources linked in the text. The feature image was generated with AI.
Related articles
- Ethereum and Quantum Computers: Are Your ETH Affected?
- Bitget Hack of $351 Million: What to Check at Your Crypto Exchange Now
- Bitcoin and the Quantum Computer: Which Addresses Already Expose Their Keys
- How to Set Up a Crypto Wallet: Securing Your Coins in Seven Steps
- Hot Wallet or Cold Wallet: the Private Key Decides How Safe Your Coins Are
Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.

August 12, 2026 5:53 PM
Bitcoin's Quantum Problem: Why 6.7 Million Coins Could Be Frozen Forever
A third of all Bitcoin sits in addresses a future quantum computer could crack. The proposed fix would lock those coins permanently. Here is the plan.

September 30, 2026 7:16 AM

Tangem Wallet: The Card Without a Seed Phrase vs the Classic Hardware Wallet
The Tangem Wallet secures crypto with two or three identical cards instead of 24 words. What the sets cost, what the EAL6+ chip delivers and why losing every card is final.
September 24, 2026 4:16 AM
Trump-Xi Summit at the White House: The Crypto Positions to Check Before the Meeting
Xi Jinping is on a state visit to Donald Trump today, and the crypto market comes into the meeting carrying the gains of an exceptionally strong week. What to check on leverage, holding period and custody before the first headline runs.
August 15, 2026 9:31 PM
Crypto Exchange Shutting Down: What to Do Before the Deadline Passes
Binance, BitMart, Luno and Revolut have ended or cut back their European business within seven weeks. This guide shows which deadline expires first, how a forced sale is treated for tax, and what to secure before the account closes.

September 24, 2026 1:34 PM
Cardano Slides Below $0.24: What ADA Holders Should Check on Leverage, Liquidation and Holding Period
Cardano has given back its move above $0.25 and trades around seven percent below the high of the past 24 hours. What that means for leveraged positions, the holding period of your tranches and the buying route under MiCA.
August 21, 2026 4:17 PM
Crypto Withdrawals to Your Own Wallet: Why Exchanges Demand Proof of Address Ownership Above €1,000
Above €1,000 your provider has to establish whether the destination address really belongs to you. Article 14(5) of the transfer of funds regulation, five permitted methods, and the reason a withdrawal stalls without this step.
August 13, 2026 4:59 PM

Trezor Data Breach: First 13,689 Customers, Then Roughly 67,000 More Exposed
A breach at Trezor shipping partner ShipMonk exposed names, phone numbers and home addresses of 13,689 customers in August; in September Trezor reported roughly 67,000 more in the US. Devices are safe, phishing risk is not.
September 7, 2026 7:26 PM

Stolen Keys Beat Code Flaws: Why the Private Key Is the Way In for 2026 Crypto Hacks
Compromised private keys overtook smart contract code flaws as the most common attack route for the first time in 2026. What sits behind the shift, and how to check your own setup for its single point of failure.
August 11, 2026 1:32 PM

How to Store a Seed Phrase Safely: What Steel, a Passphrase and Multisig Do for Your Wallet Backup
The Coldcard case pushed the manufacturer question to the front, while barely touching on where the backup is kept. This guide places paper, steel, the passphrase and splitting methods against the BIP-39 and SLIP-0039 standards.

September 24, 2026 10:11 PM

Bitcoin Price Prediction: What to Check on Levels, Holding Period and Leverage Before the October 28 Rate Decision
Bitcoin is trading at around $83,800, a third below its October 2025 high, while the sentiment index reads greed. Which dates, levels and deadlines over the coming weeks really decide your net gain, and which of them you steer yourself.
September 4, 2026 10:15 PM

Trezor Data Breach: Am I Affected and What Should I Do Now?
Trezor widened the ShipMonk data breach on September 4, 2026: around 67,000 further people affected, just over 80,000 in total, from orders placed between November 2019 and August 2021. How to check in two minutes whether you are among them, and what an exposed home address means for self-custody.
August 5, 2026 10:33 PM

$130 Million Gone Because the Randomness Was Predictable: Which Hardware Wallet You Can Still Buy
The Coldcard flaw proved the most respected wallet is not the safest. Which vendor has which track record – and why now is the wrong moment to pause your savings plan.
August 4, 2026 1:21 PM
Coldcard Losses Near $114 Million as a Fourth Sweep Hits: Why Is Bitcoin Rising Anyway?
A fourth wave of Coldcard sweeps took another 449 BTC on Monday, yet Bitcoin climbed back toward $64,000. Here is what changed and who is still exposed.
July 31, 2026 3:54 PM
594 BTC Gone in 25 Minutes: The Coldcard Flaw That Made Seed Phrases Guessable
A firmware bug from March 2021 let an attacker drain $38 million from around 500 Bitcoin wallets. Here is what broke, who is exposed and what to do now.
August 21, 2026 4:27 PM
Wallet App Without BaFin Authorisation: When Holding Crypto-Assets Requires a Licence
On 19 August 2026 BaFin published two consumer notices on wallet offerings. Who controls the means of access decides whether an authorisation is needed.
March 31, 2026 5:13 PM
Quantum Threat to Bitcoin? Google Research Sparks Urgent Crypto Security Debate
Google’s quantum breakthrough raises fears for Bitcoin security. Can crypto survive quantum attacks—or is an upgrade urgent?
August 6, 2026 3:05 PM
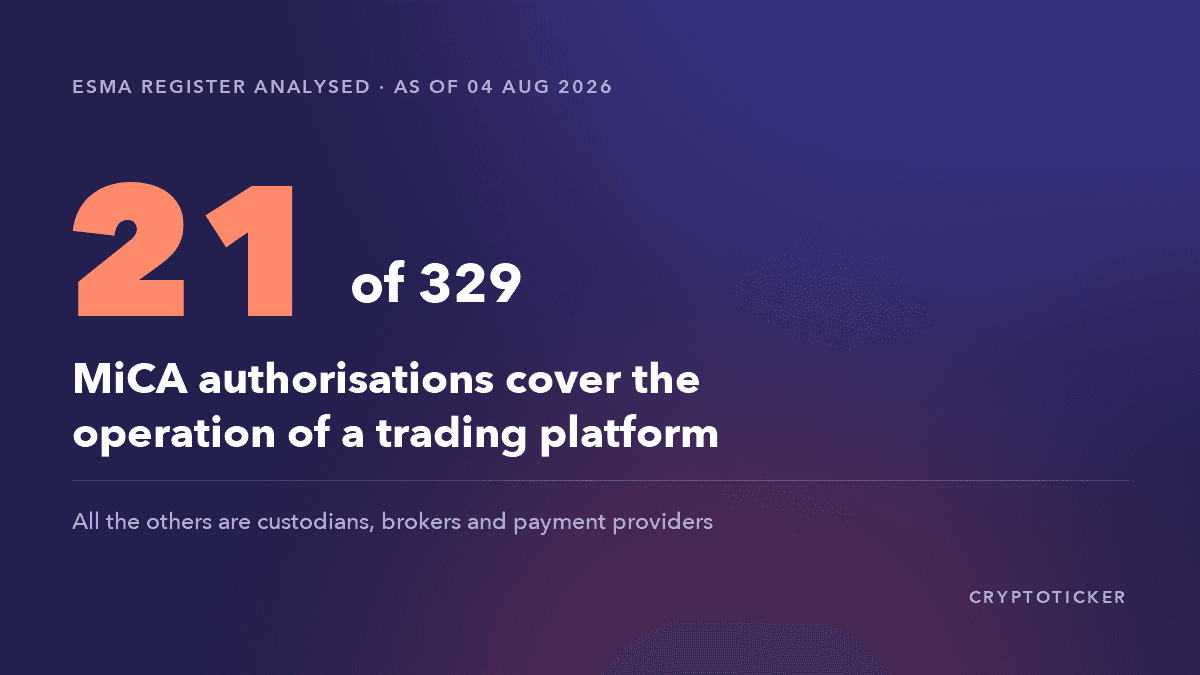
MiCA Register 2026: Only 21 of 329 Licences Are Real Exchanges
ESMA publishes the register of MiCA-authorised providers as an open file. We worked through all of it — and the result is not what the phrase “licensed crypto exchange” suggests.
September 16, 2026 1:28 PM

Crypto Withdrawal to Your Own Wallet: Ten Providers Checked, Three Will Not Let Your Coins Out
Seven of ten providers available in Germany offer a payout to a wallet address you control yourself; three do not. Our survey of September 16, 2026, shows how to spot the difference before you buy, and why the question matters right now.
August 24, 2026 1:22 PM

Phantom Wallet Ends Sui and Monad Support: What to Do Before the Deadlines
Phantom Wallet removes Monad from its app on August 26 and Sui on September 24. The balances are not lost, but only one of the two ways out leaves your tax position untouched.
August 20, 2026 4:24 PM

Bitcoin Across Multiple Wallets: How Austria Works Out the Acquisition Cost
Bitcoin spread across several wallets? How Austria works out the acquisition cost and the rolling average price for tax purposes.
July 2, 2026 8:59 PM
Binance Is Out of the EU: How to Move to a MiCA-Regulated Exchange
Binance has left the EU market. Which exchanges hold a MiCA licence, how to verify an authorisation is real, and how to move your holdings across step by step.
September 29, 2026 10:33 AM
ESMA puts reverse solicitation on its 2027 watch list: what investors need to know about exchanges without an EU licence
ESMA presented its work programme for 2027 on September 28, 2026 and made reverse solicitation a supervisory priority. What that means if your coins sit with a provider without EU authorisation, and which three steps make sense now.
September 20, 2026 4:15 PM

Crypto Phishing After a Data Breach: The Warning Signs in a Fake Exchange Email
After every major data breach, the number of phishing emails sent in the name of crypto exchanges and wallet manufacturers rises. This article shows you how to recognise such a message, which data a reputable provider never requests by email, and what to do in the first hour after a click.
September 1, 2026 7:27 AM

Clipboard Attack: How Malware Swaps the Wallet Address You Copied
A clipper replaces the receiving address between copying and pasting with the attacker’s, and your wallet’s checksum notices nothing. What Microsoft and the Federal Office for Cybersecurity have documented, and which check really makes the attack come to nothing.
April 27, 2026 10:30 AM
Win $5,000 in BTC: Tangem Launches Exclusive 2026 Prize Draw
Tangem announces a massive prize draw with $5,000 in BTC and iPhone 17s up for grabs. Secure your crypto and enter today using our exclusive link.

December 22, 2020 3:49 PM
Crypto Wallet Provider Ledger Hacked: Data Leak Results in Phishing Scams
Ledger, a cryptocurrency wallet provider has encountered a data breach. The official Twitter account of the hardware wallet tweeted that they have been alerted to the dump of a client database.
October 4, 2026 1:42 AM
Five crypto apps for beginners: costs and custody compared
Fee-free rarely means free of charge with crypto apps: between 0.15 and 2.49 percent per purchase lies a factor of ten. What five apps cost German beginners, who holds the coins and which app permits a transfer to your own wallet.
More from CryptoTicker